BlockThreat - Week 43, 2026
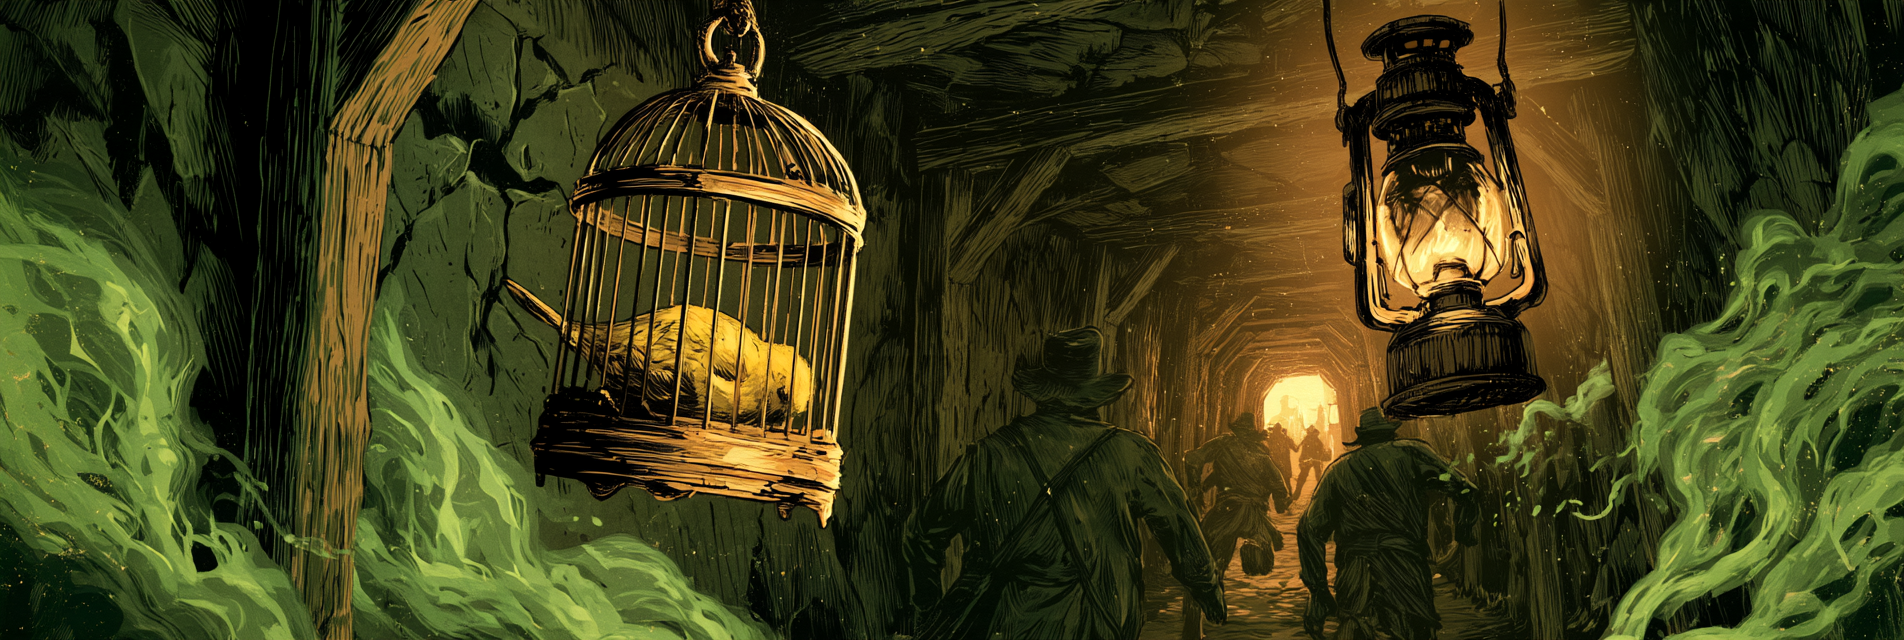
$22.3M stolen across 14 incidents. Crypto was the canary for Black October. Now the canary is coming home to roost.
Welcome to the first public good edition of BlockThreat, served completely free and open so that we can all learn from each week's tough lessons and get a bit safer together. If you're enjoying it, consider chipping in with a small contribution. As always, BlockThreat never skips an edition, so this one and the next will catch you up on everything that happened in October while I was away presenting at the DeFi Security Summit and enjoying great food and even better company in Mumbai.
Crypto security has always been the canary in the coal mine for the rest of the security world. We feel the latest attack techniques first, because compromising an exchange or a DeFi project has always been the most direct path to financial assets. So when we had our Bloody April earlier this year, the clock started ticking for everyone else. Six months later traditional security got their "Black October", when everything seemed to get hacked, from cloud providers (Railway) and certificate authorities (eMudhra) to core languages (PHP, Python, Node), services (Tailscale), and more.
While tradsec is seeing the same rise in exploitation we saw in April, they have not yet felt the dollar losses. The difference is that their hacks leak PII, while ours drain wallets. The good news is that we had six months to prepare. The bad news is that decentralized finance still runs on very centralized infrastructure. The pillaging in the wider security world is already coming for us through a spike in compromises of supply chains, backend infrastructure, frontends, signing keys, endpoints, and everything in between. See the Hacks section below for details.
The only way out is through. Despite your best efforts to lock down endpoints, supply chains, and cloud, it's now best to operate on the assumption that you are already hacked, your secrets have leaked, and attackers are busy moving through your environment. Can you rise to the challenge and build an environment that will survive two or more compromised dev laptops? What about a stolen deployment key that you forgot to put behind a timelocked multisig? The tools and knowledge to build truly resilient systems are here, but you must choose to adopt them to come out the other end stronger than ever. Will you accept the challenge or join many other projects that have already shut down this year?
Before we begin, I want to take a moment to celebrate the fantastic security research shared with the community this week such as the latest updates from The Red Guild, an honest discussion of LLM security capabilities by Antonio Viggiano (Monad), AI patching footguns by Anish Naik and Marcelo Morales (Trail of Bits), the constant stream of audit checklists and security insights by Bloqarl (Zealynx), broken assumptions in Glamsterdam by the good folks at ChainSecurity, a very cool find in Yul by d4r3d3v1l, a very concerning malware sample analysis by SlowMist, more vulnerability writeups by QuillAudits, and many more. All of this research proves again and again that nothing beats human curiosity and perseverance. Thank you for sharing. Will you join their ranks in the next edition?
And now let’s dive into the news!
News
- Ethereum’s long-awaited Glamsterdam upgrade hits another roadblock as 13 security risks emerge
- Bitcoin Core security policy update. The policy adds disclosure timelines for various severities and embargo policy.
- CoinDCX deposit address TQKJQ was in use by a LP for 10 months after your July 2025 incident by ZachXBT. $15.8M in user deposits to a compromised hot wallet address.
- Crypto mixer Railgun ignored a US lawsuit claiming it laundered North Korea's stolen crypto, and is now in default. Full complaint here.
- Back at Ekoparty: three days of blockchain, security, and community by The Red Guild. Lot's of hacker goodies inside.
News - Web2
- Preliminary Report: Oct 21st Security Incident by Railway. Slow response lead to about $371K were stolen from crypto projects as a result of the data leak.
- eMudhra CA compromise: eight private keys, and one of them is 4 - CVE-2026-111943 by Aikido.
- A tale of two PHP remote vulnerabilities by Calif Research. This story outlines the details of PHP2Shell, two PHP remote vulnerabilities (CVE-2026-109618, CVE-2026-109619) discovered by Calif, OpenAI and Wiz, and addressed in PHP October 2026 Security Release. Similar exploit also works in NodeJS, Python, and other software. Interestingly The PHP Foundation had access to both Mythos and Daybreak Red and didn't find the bug. The exploit itself proved tricky to weaponize and required skilled exploit developers.
- Tailworm. Multiple criticals in Tailscale SSH products.
- The attack chain behind the v1.107.0 LiteLLM release by LiteLLM. Be careful with Github leaks.
- Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases.
Crime - Enforcement
- Italy Targets Crypto Money-Laundering Ring Across Europe.
- Chinese Prosecutors Seek to Confiscate $5.1B in Bitcoin Seized by UK in Qian Case.
Crime - DPRK
Crime - Wrench
Phishing
- Advisory: Fake White-Hat Researchers Target Solana Protocols With Malicious Exploit PoCs by SEAL.
- Web3 Interview Questions Conceal a Data-Stealing Backdoor by SlowMist. A deep dive into vscode project malware.
- Crypto.com 3.2M Phishing Campaign July 2026 by Intelligence On Chain (IOC).
- Incident report: the fake LIQUID security alert of 17 October by NGRAVE. $2.65M were drained. Watch those 3rd party providers.
- Keystone customers say breach exposed data the hardware wallet maker promised to delete.
- I just witnessed the most involved and sophisticated phishing attempt I've ever seen by Michael Garfield.
Malware
Media
- The Quantum Security Threat with Colton Dillion & Dr. Richard Carback from Quip Protocol by Oak Security.
- 60+ initiatives. One big question: where should Ethereum security focus next? by thedao.fund
Vulnerabilities
- Fuzzing for a Solana Governance Bug by Kai Parker (Asymmetric Research)
- When the Yul optimizer forgets to forget by d4r3d3v1l. An interesting bug in Solidity's Yul optimizer.
- Forcing Recovery Through Uniswap Unlock by QuillAudits.
Contests
- Steal My Bitcoin CTF proof of concept by KillaBoi. A fully weaponized exploit against Alpine PHP server with some BTC on it. Part of a contest to see if PHP2Shell is exploitable.
- Ekoparty 2026 - Blockchain CTF by umharu.
Research - AI
- News or Hype? by Rekt.
- Evaluating Mythos 5.1 on Smart Contract Security by Antonio Viggiano (Monad). Getting to an exploitable bug is not as simple as you thought.
- Your AI agent fixed the bug, but what else did it change? by Anish Naik, Marcelo Morales (Trail of Bits).
- Inside Cairn: Open Windows into massive AI-Driven Cyber Operations by NorForge.
- AI Agent Wallet Security: 5 Ways Someone Empties It (and the Fix for Each) by Bloqarl (Zealynx).
- LLMs are making formal software verification feasible at a much larger scale by Anthropic.
Research - Bug Hunting
- Capital intensive AI bug bounty hunting is a doomed by LonelySloth.
- What I would do today if I was starting from scratch in web3 bug bounties by Alex the Entreprenerd.
Research - EVM
- Glamsterdam Hard Fork: When Spent Gas Comes Back by ChainSecurity.
- EIP-7702 Security: 5 Delegate Contract Bugs and the Fix for Each by Bloqarl (Zealynx).
Research - Chain
Whitepapers
- Can Trustless Agents Be Trusted? An Empirical Study of the ERC-8004 Decentralized AI Agent Ecosystem
- ABF-Bench: A Verifiable Benchmark for Agentic Blockchain Forensics
- Empirical Analysis of TEE-Enabled Rollup Designs
- Who Patches the Lightning Network? Evidence from Release Lines in Gossip, 2023-2026 by Saurabh Kumar
- PQ-Vault: Provably Quantum-Safe Asset Custody for Unmodified Ethereum by Hassan Khodaiemehr, Khadijeh Bagheri, Chen Feng
Tools · AI
- Security Audit Skill by Cloudflare. A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings.
Hacks
Detailed indicators of compromise including exploit transactions, attacker addresses, additional write ups, exploit PoCs are available upon request.
Argent-Style Smart Wallet Compromise
Date: October 19, 2026
Attack Vector: Signature Verification
Impact: $59,800
Chain: Ethereum
https://x.com/SlowMist_Team/status/2112157232624476254
Vara Bridge Compromise
Date: October 19, 2026
Attack Vector: Signature Verification
Impact: $13,000
Chain: Ethereum
https://x.com/VaraNetwork/status/2113620599054733345
Keystone Compromise
Date: October 20, 2026
Attack Vector: Server Compromise
Slice Compromise
Date: October 21, 2026
Attack Vector: Fake Deposit
Impact: $41,000
Chain: Base
https://x.com/TenArmorAlert/status/2112714662064398524?s=20
Swell Compromise
Date: October 21, 2026
Attack Vector: Stolen Private Keys
Impact: $3,200
Chain: Arbitrum, Base, Ethereum, HyperEVM
https://x.com/swellnetworkio/status/2113103884885561610
Fearless Wallet Compromise
Date: October 21, 2026
Attack Vector: Code Injection
Impact: $20,000
Chain: Polkadot
https://x.com/Polkadot/status/2112910039207800970
NEM (Newmont) Compromise
Date: October 21, 2026
Attack Vector: Reward Manipulation
Impact: $821,920
Chain: BSC, Ethereum
https://x.com/SlowMist_Team/status/2113206749524316486
CoinDCX Compromise 2
Date: October 22, 2026
Attack Vector: Hot Wallet Compromise
Impact: $16,000,000
Chain: Ethereum
https://x.com/zachxbt/status/2113191832561778974
Initia Compromise
Date: October 23, 2026
Attack Vector: Consensus Failure
Impact: $2,700,000
Chain: Initia
https://ourcryptotalk.com/news/initia-iusd-backing-restored-after-exploit
Arkadiko Compromise
Date: October 23, 2026
Attack Vector: Governance
Impact: $1,090,000
Chain: Unknown
https://x.com/ArkadikoFinance/status/2113367201722044512?s=20
Electrum Wallet Compromise
Date: October 24, 2026
Attack Vector: 3rd Party Compromise
Chain: Bitcoin
https://github.com/spesmilo/electrum/security/advisories/GHSA-6jp4-8v48-cc5v
N On Nexus DotSwap V1 Compromise
Date: October 25, 2026
Attack Vector: Signature Verification
Impact: $685,000
Chain: Bitcoin
https://x.com/swap_on_nexus/status/2114918342863868103
Zilliqa X-Bridge Compromise
Date: October 25, 2026
Attack Vector: Consensus Failure
Impact: $845,000
Chain: Ethereum
https://x.com/plunderswap/status/2113507036772368693
Yapeswap Compromise
Date: October 25, 2026
Attack Vector: Governance
Impact: $22,000
Chain: Ethereum