BlockThreat - Week 38, 2026
$33M stolen across 13 incidents. Yoinking tokens from blackhats. SinglularityNET mass compromise. Hacks are getting weirder.
SingularityNET Bridge Mass Compromise
On September 19 an attacker compromised multiple asset singing keys held on SinglularityNET bridge and went on the token minting rampage targeting FetchAI, NuNet, Cogito, World Mobile tokens. Total take was about $2.3M. This incident is a really good reminder that if your project trusts a singing key to a 3rd party then your security model is that 3rd party's opsec. A few takeaways:
- There is no reason a 3rd party can mint unlimited tokens in a short window.
- Whatever limits you put in must be enforced on all exit points so attackers can't just bypass them like they did with uncapped
conversionInon FET. - Watch 3rd party dependencies for signs of compromise so you can hit that pause button before attackers get you as well. There was a small window when the second wave hit that pointed to SingularityNET bridge compromise.
- All 3rd party dependencies should be in your threat model including shared incident response channels and a detailed discussion of security practices.
Yoinking $7.8M from a Safe Module Hacker
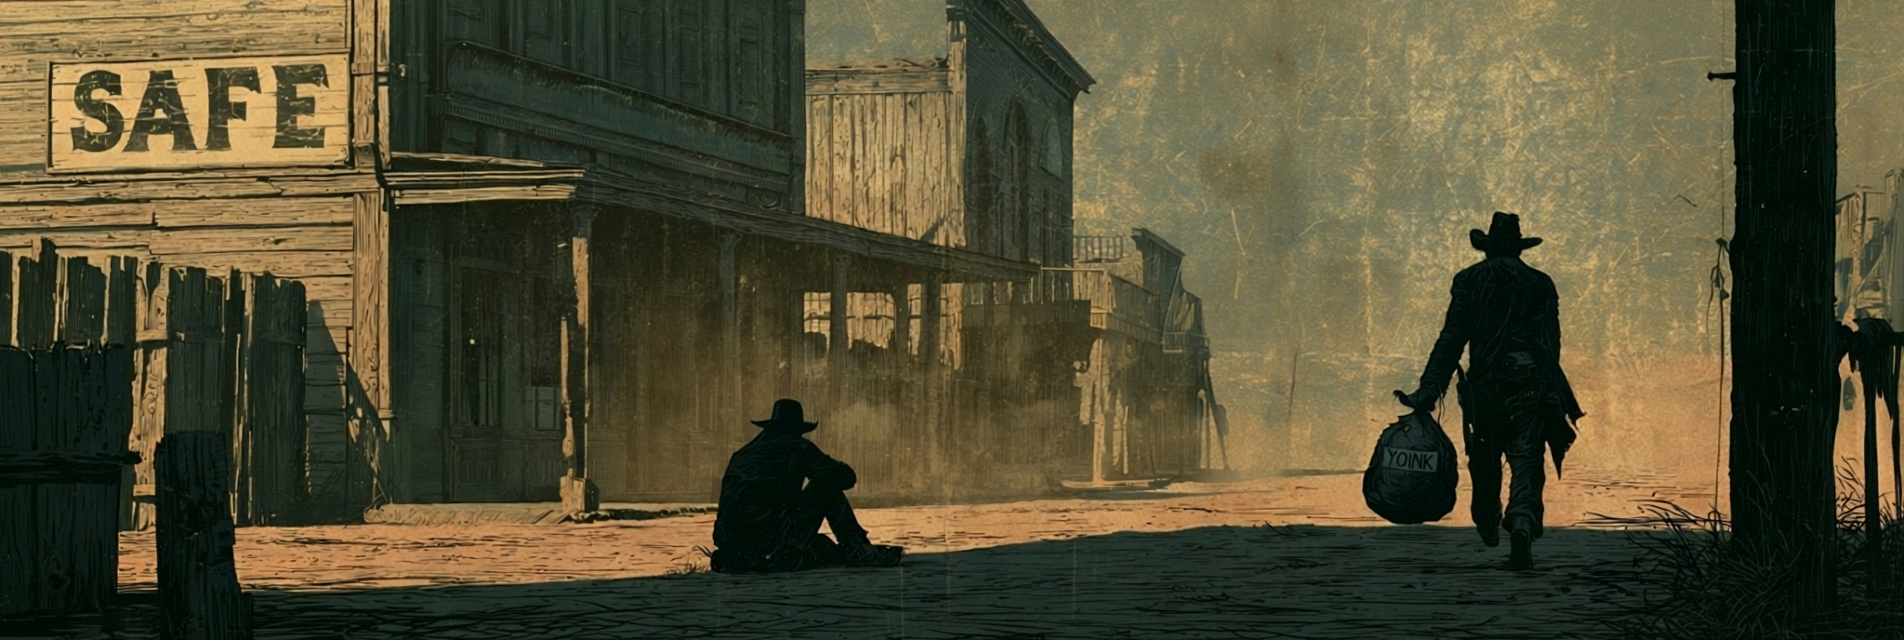
In the cloudy skies of blockchain exploits we sometimes get a glimmer of light. This week it came from a hapless exploiter who found a weak Safe wallet module, built a working $7.8M exploit, and then broadcast it to the public mempool, where an MEV bot yoinked the whole haul from right under their noses. A blackhat gunslinger lost to a faster gunslinger, which is about as close to a happy ending as the DeFi frontier gets. It is also a reminder of one of the many defensive capabilities our ecosystem has barely begun to use.
AI Hunters are Feasting
Attackers keep showing up in ecosystem that rarely got a security look in the past. DCENT mobile app wallet is tracking $18.8M in drains, MultiversX halted their chain to stop a consensus exploit, Nimiq blockchain had a signature vulnerability. The hacks involve more and more obscure projects and protocols. If your ecosystem relied on security by obscurity know that the time it takes for a blackhat to get up to speed on your codebase has gone from months or weeks to hours. Welcome to the brave new world of AI bug hunting.
In the rest of this week's edition, we cover Vitalik's thoughts on AI hacking, Trail of Bits on auditing in the age of "good enough" models, a hands-on course for building your own bug-hunting harness, and much more. Wallet builders getting slammed right now should check out Coinspect's new tool for hunting weak key generation and much more.
That's 80 carefully curated reads, 15 new whitepapers, 6 tools, and 13 incidents worth your time. Attackers are already reading the same papers, using the same tools, and studying the same incidents, week after week. For about $3 an edition you'll know everything they know.
Let’s dive into the news!