BlockThreat - Week 35, 2026
$145.3M stolen across 15 incidents. Two mass-exploitation campaigns remain active. $120M+ stolen using an almost forgotten attack vector.
It's blood on the streets again. This week I’m tracking two mass exploitation campaigns across Cosmos and Solana. The quieter story is the attack vector that just came back and claimed combined $120M+ in just a few days. The issue includes details of how all of these campaigns unfolded, why the forgotten attack vector belongs on every audit and ops checklist now, and the lessons auditors and defenders should adopt immediately. This week's edition includes latest case studies, vulnerability reports, research, tooling, and write ups for all 15 incidents.
Let’s dive into the news!
Cosmos Mass Compromise
Continuing the alarm we raised last week, the Cosmos mass compromise continued widening with now six different networks exploited including Mantra, TAC, KiiChain, Nesa, and others. Attackers stole about $12M across multiple incidents so far; however, this could have been much worse.
According to the recently published post-mortem, the original vulnerability report came in April, but the bug was misclassified as not exploitable. A silent fix was published later in May. However, the recent exploitation frenzy came after Push Chain published a PR detailing the exploit chain.
There are a number of lessons from this incident, but the few most critical are:
- There is no such thing as silent patch. Open or closed source attackers are watching new releases for any signs of 1day vulnerabilities and get busy at weaponizing the exploit against any targets that did not yet patch. This is especially concerning as the recent time to build a fully functioning exploit is in the hours rather than days or weeks as it was in the past.
- The silent patch came from Cosmos maintainers misjudging the severity of the reported issue which prompted them to release the patch with no urgency (a month later) or launching a private disclosure process.
- Chain operators must know their dependencies and risk associated with them. The $7.5M TAC and $162K Enjin exploits should not have happened if only they paid attention to ongoing ecosystem incidents and responded appropriately after other Cosmos chains were compromised.
When It Rains, It Pours
Speaking of mass compromises, a vulnerability in an outdated Rain Solana contract triggered a mass hacking frenzy across crypto-card programs. A failed signature validation of Ed25519 instructions misplaced trust to attacker controlled key. This allowed attackers to get privileged authority over customer accounts and steal funds.
Avici, Tria, and other projects were hit for almost $1M after attackers compromised thousands of accounts. Luckily, multiple projects promised to make users whole, so this became another expensive lesson in 3rd party dependencies.
Avi is Back?
The previous two mass-compromise events got most of our attention. However, I am most concerned about three separate incidents last week all involving an attack vector we had almost forgotten about from the previous bear market.
A traditional DeFi exploit usually targets a logic error in code to drain a protocol in a few transactions. Economic attacks play a longer game. The attacker studies how a protocol values collateral, where its oracle obtains prices, how much liquidity supports those prices, and how the protocol interacts with the rest of the ecosystem. They then manipulate one of those assumptions, with their own money at stake, until the system produces a “highly profitable trading strategy.”
Avi Eisenberg’s infamous $116M Mango Markets exploit remains the case study for these kinds of exploits. Back in 2022, Avi and his team established a large perp position and drove up the price of the thinly traded MNGO token. The protocol treated his unrealized profit as collateral and let him borrow $110M of assets.
Last week brought three variations on the above strategy:
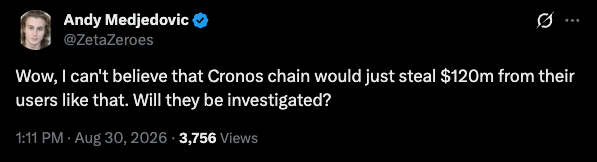
- Tectonic attackers pushed the TONIC token up about 100x and borrowed $75M against inflated collateral.
- Moonwell attackers similarly pumped MAMO token only to run off with a $11M loan.
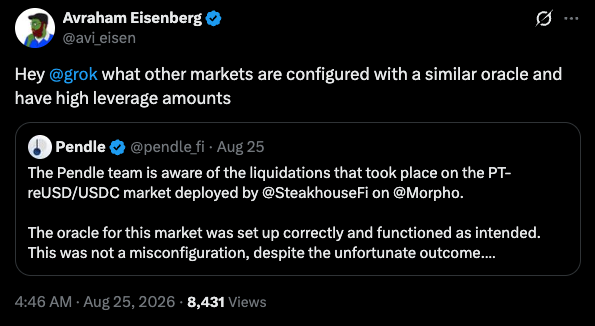
- Steakhouse experienced the inverse price action where attackers bought up the PT-reUSD token, pushed its price down, and triggered $36M of liquidations.
Mango Markets exploit and the three hacks last week exploited weak economic assumptions where prices could be manipulated with a relatively small amount of capital. While this wave is not necessarily a coordinated campaign, it does point to increase in exploitation of a fairly complex and risky to execute economic attack vector that we should all be considering during audits, protocol design, and operations.
As a side note, these incidents are already attracting some of the worst threat actors in this space:
News
- 2026 State of Crypto Security Report by CoinGecko.
- BitcoinIRA, iTrustCapital accused of hiding data breaches.
- Cosmos Labs under fire over disclosure of bug affecting four blockchains. Official postmortem admits a botched disclosure and six chains affected: Cosmos EVM GHSA-7g4w-cg88-2cq2 Post-Mortem.
- No Fork Required: Bitcoin’s First Quantum-Safe Transaction Just Happened.
- Kraken Says ‘Dust Attack’ From Sanctioned HTX Wallet Locked Out Customers.
News - Web2
- The Hugging Face incident and the road ahead by OpenAI.
- The Rise and Fall of Agent Civilizations by Dwarkesh Patel. More on OpenAI/HuggingFace incident.
- Brief independent investigation of agents’ behavior, reasoning and collaboration in the OpenAI / Hugging Face hacking incident.
- After Their AI Models Hacked Real Companies, AI Labs Call for Stronger Cyber Defenses.
Crime - APTs
- July 2026 Threat Trend Report on APT Attacks (South Korea) by ASEC.
- Insights into Suspected DPRK Workers by Huntress.
- Unmasking TeamPCP, King of Software Supply Chain Attacks.
- University Leak Exposes Russia’s Military Cyber Training Pipeline.
- Sanctioned Ravin Academy Is Training Its Biggest Class Yet.
Crime - Wrench
- Rekt - Total Exposure.
- Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total by ZachXBT.
Phishing
- The address labeled Bofur Capital got hit for $2M via address poisoning after withdrawing from #Compound by PeckShield.
- 15 victims have lost a combined $9.4M to an address poisoning attacker over the past 4 weeks by Specter.
Scams
- A fraud ring seized realtrumpcoins[.]com and the @realtrumpcoins1 account, then maliciously launched $GOLD by GoPlus Security
Malware
- Skimming on the Blockchain: A Magecart Campaign That Uses EtherHiding, Found by Malvertising Scanning by Confiant.
- The StealC Info-Stealing Chain Behind the Qwen Impersonation Repository by SlowMist.
- 77 Firefox Extensions Linked to Crypto Wallet and Credential Theft by Socket.
- If you use Claude, you could LOSE your crypto to malware without ever knowing you were hacked by Coin Bureau.
Media
- Oak Security - Security at Arbitrum with Lorenzo Sicilia.
Vulnerabilities
- Eight Bytes to Burn a Bridge - Relay Protocol’s Legacy Bitcoin Sighash Bug by Zellic.
- Lido – Missing pending top ups in CL pending balance calculation by Composable Security.
- Privacy Pools SDK Bug Patch and Key Migration by Privacy Pools.
- State divergence enables unauthorized access by Trail of Bits. A bug in Provenance blockchain, a Cosmos SDK chain.
- Every Ledger running the Ethereum app is vulnerable to signature substitution by TestMachine. More details.
- Ledger's Clear Signing Race: One Extra APDU Could Swap the Transaction You Approved by SigintZero.
- Core Lightning confirms multiple vulnerabilities, prepares security update.
Research - Bug Hunting
- Web3SecSummit: traditional EVM fuzzers plateau at 73/153 Daedaluzz bugs; AI-guided harness clears the set by Michal Převrátil (ack3ai).
- Security Research Without Asking Permission by Niels Provos.
- A Test Suite Can Execute Every Line Of Your Contract And Detect Nothing by Channi Greenwall.
- VMs won't contain cyber-capable agents by Artem Dinaburg (Trail of Bits).
- I accidentally turned LLM memory into program analysis by Jordy Zomer.
- Awesome Large Language Models for Vulnerability Detection by huhusmang.
Research - EVM
- The Hidden Journey: From 'Send ETH' to Blockchain Consensus by Gareth Larkan (Sigma Prime).
Research - Cosmos
- The Cosmos EVM incident gets harder to explain as a simple missed-upgrade story when you put the dates in order by Grey Ledger.
- Printing Infinite Money on the Cosmos Blockchain by Daniele Berardinelli.
- Exploit Breakdown: Cosmos EVM exploits hit in rapid succession, draining $17M+ by GoPlus Security.
Research - AI
- The journey of a failed autonomous AI vulnerability hunter by pwnh4.
- AI for Web3 Security: A Field Guide by 0xasen.
- Do LLMs get another capability jump, or just steady iterattion? by Josselin Feist.
- Vulnerability Research Prompt Based On Leaked OpenAI's CDC Prompt by SunSec. Link to the full prompt. Source: Exploit brokers pay $500,000 for a WordPress RCE. I found one with GPT5.6 Sol Ultra and $25 by Adam Kues (Searchlight Cyber).
Research - Defenders
- Can a sufficiently powerful quantum computer forge the signatures used to authorize Bitcoin and Ethereum transactions? by a16z crypto.
Whitepapers
- Mitigating Error Propagation in Chain-of-Thought: A Tree-of-Thought Framework for Smart Contract Repair.
- Defending the Peg: Real-Time Dynamic Protection and Anomaly Detection in DeFi Stablecoins.
- Information Flow Control in Off-Chain Components.
- Sei Labs paper: on-chain secret reveals enable censorship and rebinding, not just replay by @Sei_Labs.
- Giving AI Agents Access to Cryptocurrency and Smart Contracts Creates New Vectors of AI Harm.
Tools
- Immunefi Bug Bounty Programs (Unofficial) by infosec-us-team. Every time a Bug Bounty Program in Immunefi modifies its policy, assets-in-scope, or bounties-table, a bot will commit those changes to this repo.
- entropylab by w-s-bitcoin. A fully offline, air-gapped Bitcoin key and wallet calculator. It turns user-supplied entropy, seed phrases, or private keys into BIP39 seeds, xpubs, descriptors, addresses, and recovery data, and can also build watch-only multisig wallets without exposing private keys online.
- app-seed-tool by LedgerHQ. A Ledger application that provides some useful seed management utilities
Tools - AI
- cdsecurity-skills by CDSecurity. Claude Code skills for smart contract security.
- reverse-skill by zhaoxuya520. A collection of reverse engineering, malware analysis, penetration testing, security research skills.
- Pentest Harness by S1N6H. An open-source, dark-first AI agent harness for authorized penetration tests, bug bounty research, security labs, and CTF engagements.
- ZeroSkills by zerocoolailabs. A curated collection of high-signal, zero-shot detectors maintained by Zero Cool.
- numasec by Francesco Stabile. The open source AI security agent. Run security workflows with your local tools, agents, runbooks, findings, evidence, replay and reports.
Hacks
Detailed indicators of compromise including exploit transactions, attacker addresses, exploit PoCs are available upon request.
Nesa Compromise
Date: August 24, 2026
Attack Vector: Infinite Minting
Impact: $60,000
Chain: Cosmos
https://x.com/nesaorg/status/2091915864497066077
TAC Compromise 2
Date: August 24, 2026
Attack Vector: Infinite Minting
Impact: $7,500,000
Chain: Cosmos
https://x.com/TacBuild/status/2091312709438444021
Enjin Compromise
Date: August 25, 2026
Attack Vector: Uninitialized Contract
Impact: $162,000
Chain: Ethereum
https://x.com/DefimonAlerts/status/2092331652882002208
Realio Compromise
Date: August 25, 2026
Attack Vector: Stolen Private Keys
Impact: $6,200,000
Chain: Ethereum
https://x.com/realio_network/status/2092288120918044688
Steakhouse Financial Compromise
Date: August 25, 2026
Attack Vector: Price Oracle Manipulation
Impact: $36,000,000
Chain: Ethereum
https://x.com/pendle_fi/status/2092171615631249863
FH Token Compromise
Date: August 26, 2026
Attack Vector: Reward Manipulation
Impact: $20,000
Chain: BSC
https://x.com/SlowMist_Team/status/2092457395666751707
CashCowCoin Compromise
Date: August 27, 2026
Attack Vector: Price Oracle Manipulation
Impact: $117,400
Chain: BSC
https://x.com/DefimonAlerts/status/2093248983942467612
Moonwell Compromise 4
Date: August 27, 2026
Attack Vector: Price Oracle Manipulation
Impact: $8,730,000
Chain: Base
https://x.com/exvulsec/status/2092912846036402674
Ajna Protocol Compromise 2
Date: August 28, 2026
Attack Vector: Reward Manipulation
Impact: $775,000
Chain: Ethereum
https://x.com/DefimonAlerts/status/2093632180656263283
Rain Card Mass Compromise
Date: August 28, 2026
Attack Vector: Signature Verification
Impact: $1,100,000
Chain: Solana
https://x.com/CertiKAlert/status/2093428949334266091
Switchboard Compromise
Date: August 28, 2026
Attack Vector: Stolen Private Keys
Impact: $4,942,000
Chain: IOTA
https://x.com/Virtue_Money/status/2093733984463470671
Fogo Compromise
Date: August 29, 2026
Attack Vector: Stolen Private Keys
Impact: $3,880,000
Chain: Fogo
https://www.theblock.co/news/defi/2026-08-29-layer-1-blockchain-fogo-halts-mainnet-after-attacker-receives-400-million-fogo-tokens-10-of-circulating-supply-413064ZIGChain Permapod Compromise
Date: August 29, 2026
Attack Vector: Reward Manipulation
Impact: $600,000
Chain: Cosmos
https://x.com/rarma_/status/2093983756768133130
Balancer Compromise 4
Date: August 30, 2026
Attack Vector: Rounding Error
Impact: $234,000
Chain: Ethereum
https://x.com/SlowMist_Team/status/2094272540193722744
Tectonic Compromise 2
Date: August 30, 2026
Attack Vector: Price Oracle Manipulation
Impact: $75,000,000
Chain: Cronos